You have to know who you are dealing with before you deal with them, and the record of how you found out is part of the obligation. Your firm has been a reporting entity since 31 March 2026, a business that provides a designated service and so carries AML/CTF obligations. Since 1 July 2026 you must establish the identity of your customer before you provide that service. The Act puts it in those words at s28.
If you have read older guidance, put one term aside. Safe harbour is not part of the current law. It was a set of prescriptive procedures in Chapter 4 of the AML/CTF Rules 2007, and that chapter was repealed from 31 March 2026, when the AML/CTF Rules 2025 commenced. What replaced it is risk-based: you verify as much of the customer’s information as is appropriate to their money laundering and terrorism financing risk (s28(3)(d)), and you carry the judgement rather than a checklist. One bridge remains: until 31 March 2029, the Transitional Rules (ss 7 and 8) let your policies keep using customer identification procedures that met the old Rules, for classes of customer the policies name and with a date each class stops.
A designated service is a service the Act lists in its tables, set out in s6. Each table names the customer of the service, and a prospective customer counts (s5). That person is who the obligation attaches to, rather than whoever happens to be in the room.
Customer due diligence is the whole of that work: collecting identity information, verifying it against a source you can point to, and recording how you did it. The point of the exercise is that the person you think you are dealing with is the person you are actually dealing with, and that you can show how you know. Collection is where most firms are comfortable. The other two parts are where compliance actually happens, and where the rest of this page spends its time.
What you collect, how you verify it, what you keep
For an individual, collect full name, any other name they are commonly known by such as a former or anglicised name, date of birth, residential address, and a unique identifier if they have one: a passport number, driver licence number or foreign national identity number. The point of that list is to tell your customer apart from someone else with a similar name.
What you then have to verify is a judgement, not a fixed list. The Act asks you to verify, using reliable and independent data, as much of that information as is appropriate to the customer’s money laundering and terrorism financing risk (s28(3)(d)), and, for an individual, to take reasonable steps to establish they are who they claim to be (s28(3)(a)). For most individuals that starts with full name and date of birth, because those details stay with a person across a lifetime. Neither the Act nor the AML/CTF Rules 2025 prescribes particular documents. AUSTRAC’s guidance gives examples of how you could verify an individual’s name and date of birth:
| Example route | Example documents |
|---|---|
| A government-issued primary photographic document, such as a current driver licence, passport, proof-of-age card or foreign national identity card | One such document |
| A primary non-photographic document, such as a birth certificate, citizenship certificate or concession card | That document, plus a secondary one showing name and address, such as a utility bill or a notice from a government body |
An electronic check that confirms name and date of birth against a primary photographic document can do the same job as sighting it. For a low-risk individual, one photographic document, or its electronic equivalent, is a common approach. Higher risk means going further, and that judgement is yours to make and to record.
For a company, a trust or a partnership, identification extends past the entity to its beneficial owners, the natural persons who ultimately own or control it. Where you can stop digging into a structure is the question on the beneficial ownership page.
| Customer type | What identification reaches |
|---|---|
| Individual | The person |
| Company | The company’s name and registration details, plus each beneficial owner as an individual |
| Trust | The trust, the trustee, and the beneficial owners as individuals |
| Partnership | The partnership, the partners, and the beneficial owners as individuals |
All of it has to be done before the service is provided. In practice that means before you act on the customer’s instructions, not before you finish the paperwork on the day. Identification is a condition of providing the service at all, not an admin step you can catch up on later. A narrow, conditional allowance for conveyancing buyers, where verification can continue after the work begins (no later than 28 days after exchange or 3 days before the initially agreed settlement day, whichever is earliest), is covered on the delayed CDD page; treat it as an exception to plan around, not a reason to defer.
Collecting a document is not verifying it. Verification means checking the identity information against a reliable, independent source and satisfying yourself that the document is authentic and belongs to the customer. A photocopy in the file does none of that by itself: the document has to be inspected, matched to the person presenting it, and the match recorded. Most firms verify electronically, because the source is independent of the customer; a document the customer hands you is only as good as your check of it.
Because the standard is risk-based rather than prescriptive, there is no procedure you can follow to the letter and stop thinking. The obligation is an outcome: establish who the customer is. A low-risk individual with a current passport is quick. A customer with a layered corporate structure, or one who trips a risk factor, is not, and the file has to show you went further because you decided the risk called for it.
That cuts both ways. Nothing certifies your method in advance, so the burden of showing it was adequate sits with you. But nothing confines you to a fixed document count either, which is what the old Chapter 4 procedures did. Whichever route you take, the record must show which one it was and why, because the method is the first thing a reviewer looks for.
Identification is also only the start. The relationship needs attention while it is live, and some customers trigger enhanced customer due diligence (ECDD), a deeper set of checks covered on the enhanced due diligence page.
What you record matters as much as what you verify. For every customer the file should hold the identity information collected, the evidence it was checked against, the route you took and why, the source reference IDs such as document numbers, who did the work and when, and the outcome. The decision about which method to use, and why, is itself a record. The file has to be reconstructable by someone who was not there, which is why the evidence itself matters, not just a tick next to the customer’s name. All of it is retained for seven years, and the full shape of that obligation is on the record-keeping page.
One shortcut exists, with conditions attached. Where another reporting entity has already verified the customer, you can rely on that work instead of repeating it; what the arrangement requires, and what liability stays with you, is on the reliance page.
What catches people out
-
A label is not a method: firms record that a customer was “verified” without recording what was actually done, often carrying the habit over from the old Chapter 4 tick-box. Under a risk-based standard the label carries nothing on its own. If the file does not show the check, the source and why it was proportionate to the risk, AUSTRAC reads the customer as unverified. The consequence shows up at review, not at the time of the check.
-
Collecting a document is not verifying it: the classic failure is a file full of passport copies that were received but never inspected, never matched to the customer, never checked against the source that issued them. When a reviewer looks, every one of those customers is unverified, and you cannot show you took reasonable steps at the time.
-
The record of how you verified matters as much as the outcome: two firms can verify the same customer to the same standard. The firm whose record shows the method, the sources and the evidence gets credit for it; the firm whose file is bare does not. Seven years is a long time for a record to survive, and if the person who ran the checks leaves, the evidence goes with them unless the file stands alone.
What is still unsettled
Two points are still settling.
How firms apply the per-entity requirements is still settling. The AML/CTF Rules 2025 set minimum information to collect for some customer types, such as sole traders, bodies corporate, partnerships, associations, trusts and government bodies (Rules 6-1 to 6-4), but how much of it each firm verifies, and with what evidence, is still being worked through by firms and advisers. Build your collection workflow against the Rules and the reform guidance and expect to adjust it.
How far is far enough is the second, and it is the cost of a risk-based standard. The old regime told you to sight two documents and stop; this one asks you to establish identity and leaves the sufficiency to your judgement. AUSTRAC has not published worked examples of what an adequate record looks like at each risk level. Until it does, the safest record is the one that would convince a reviewer who was not there: what you checked, against what source, why that was proportionate to the risk you assessed, by whom and when.
Where to start
If you have not set up customer due diligence yet, start here:
- Map your customers: work out which of your services are designated services and who the customer of each one is under the Act’s tables. Each of those people and entities needs a file before you serve them.
- Choose the method path first: decide how you will verify, electronically against an independent source or manually against documents you inspect, and at which risk levels each applies. Write the decision down before the first customer. The choice cannot be reconstructed after the work.
- Record at the point of verification: capture the method path, the source reference IDs and the evidence while you do the check. Make the seven-year retention the named responsibility of your AML/CTF compliance officer (the AMLCO).
How duely handles this
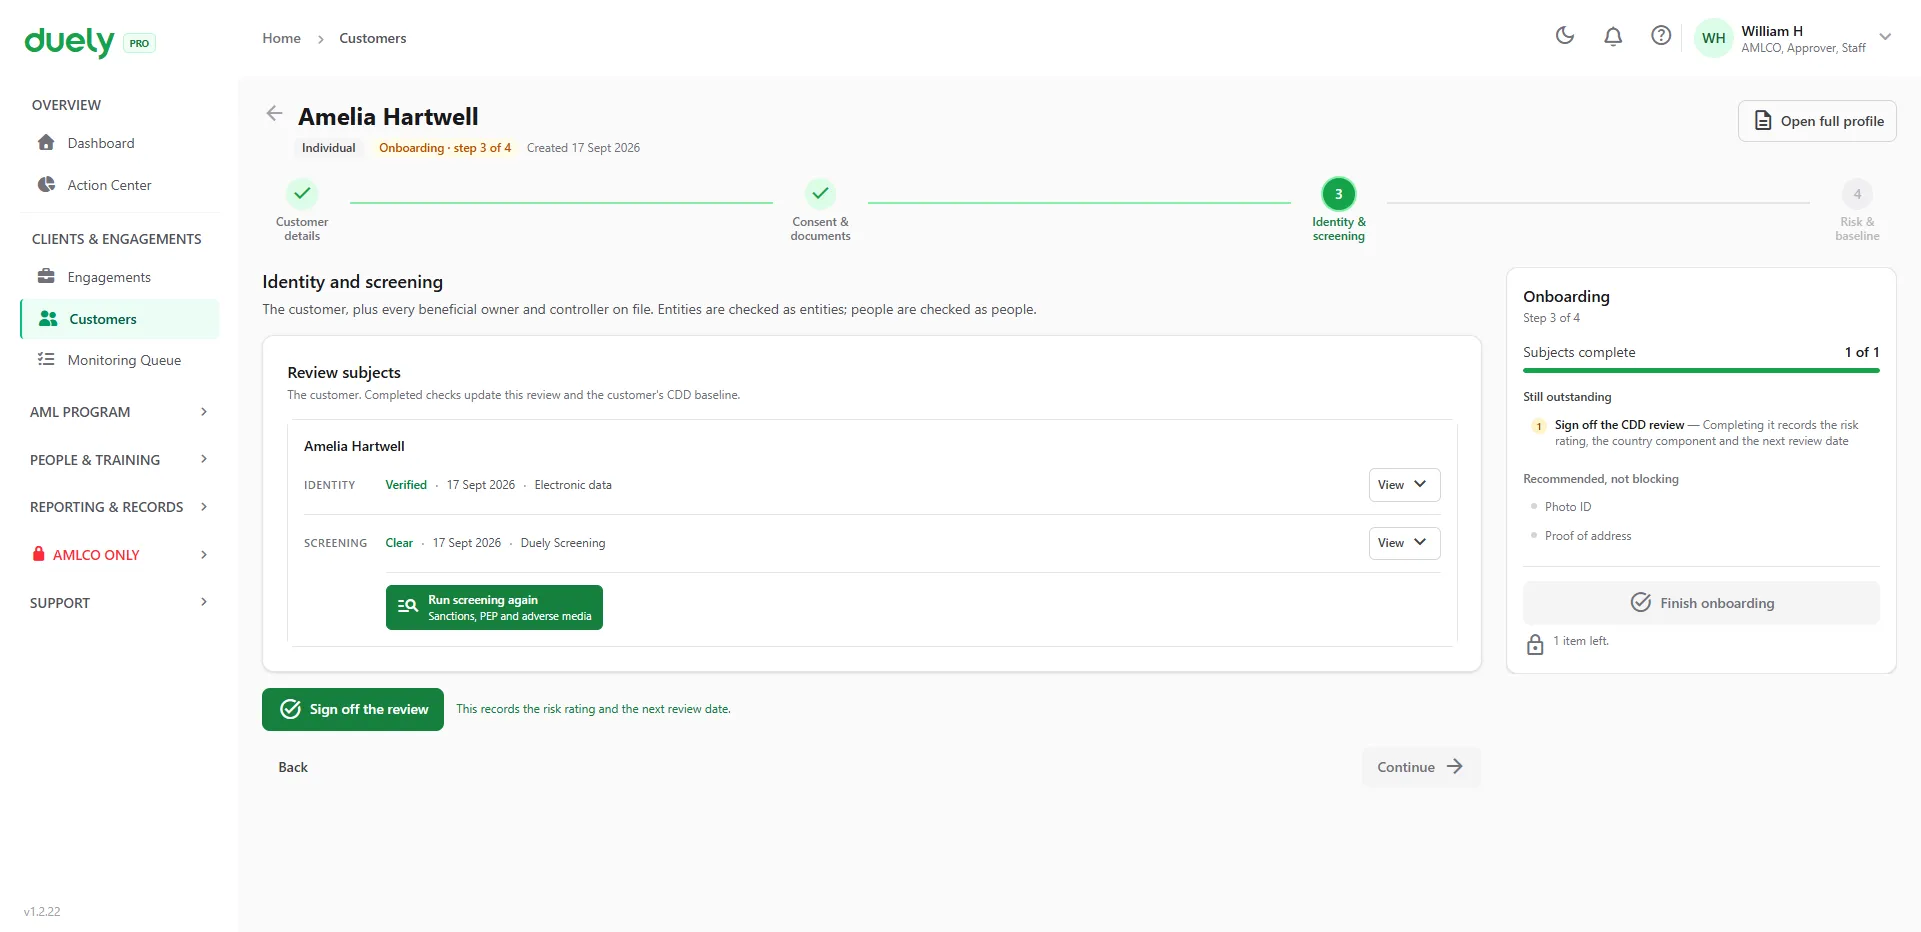
The verification gate is the part worth knowing about. A check that has not actually been satisfied can never be marked as verified in duely: the status is derived from the evidence on the record rather than set by hand, so an engagement cannot proceed on someone’s assurance that the ID was fine. Verification runs either as a link you send the customer, which they complete themselves, or as a structured manual check your staff record with the evidence attached. Either way the method, the source references and the person who did the work are all part of the record.