Record-keeping is the obligation that answers a reviewer’s first question: what did you do, and can you show it? You hold the records for seven years, the count starts from a different point for each record type, and the file has to survive the person who created it.
You have been a reporting entity since 31 March 2026: a business the AML/CTF Act 2006 (Cth) captures and holds to its obligations. That happens when you provide a designated service, one of the services the Act lists as captured. For a law practice, Table 6 of the Act covers assisting in a conveyance and creating or restructuring a company or trust. Accountants, conveyancers, real estate agents, dealers in precious metals and stones, and trust and company service providers have their own lists. Enrolment opened on 31 March 2026, and the obligations started on 1 July 2026, so record-keeping applies now. Whatever your sector, the obligations start producing records from your first customer.
The rule itself is short: records are retained for seven years. Everything else is detail, and the detail is where firms come unstuck.
What you keep, and from when the seven years runs
Start with what counts as a record, because the set is wider than the documents you collected. If you verified a customer’s identity, the driver licence or passport scan is a record, and so is the note of how you verified it, the method you used, and why you accepted it. If you assessed a matter and decided it did not need reporting, the reasoning behind that decision is a record. A reviewer reads the reasoning as closely as the document, because that is where compliance shows.
The retained set falls into several groups, and each section of the Act sets its own anchor. Transaction records and the documents customers give you are the everyday ones. Customer due diligence (CDD), the process of collecting and verifying a customer’s identity before you provide a designated service, produces the largest. Program records show how you met your AML/CTF program obligations. Reports you lodge with AUSTRAC, a suspicious matter report (SMR) when you form a suspicion on one of the grounds in s 41(1) and a threshold transaction report (TTR) for cash of $10,000 or more, have no retention section of their own: the records behind them are kept under whichever section covers them. Seven years is the term; the anchor is the variable.
| Record type | What to keep | Retention period |
|---|---|---|
| Transaction records | Enough to reconstruct each transaction in providing the service | Seven years from the day the record is made (s 107) |
| Documents the customer gives you | The document about the service, or a copy | Seven years after it was given (s 108) |
| Customer due diligence (CDD) records | Records reasonably necessary to show you met your CDD obligations: identity information you collected and verified, the verification evidence, the method path and source references, and your risk analysis and decisions | Until seven years after the business relationship ends, or after you complete an occasional transaction (s 111) |
| Records given to you by a firm you relied on | The copy of its record of the procedure | Until a seven-year period passes in which you provide no designated service to the customer (s 114) |
| Reliance agreement assessments | Your written s 37B assessment | Seven years after you prepared it (s 114A) |
| Program and compliance records | Records reasonably necessary to show you met your AML/CTF program obligations: the program, the risk assessment, and records of reviews and approvals | From when the record is made until seven years after it is no longer relevant to showing that compliance (s 116) |
| SMR and TTR records | The report, the grounds and the reasoning, and for a TTR the transaction details | No separate section: keep each record under s 107, s 111 or s 116, whichever covers it, and for the longest period that applies |
The retention obligation sits in ss 107, 108, 111, 114, 114A and 116 of the Act: s 111 for CDD records, s 116 for the records showing your AML/CTF program obligations under Part 1A are met. The seven-year term is settled, and so is the anchor for each group. The form requirements are set out in the Act and the AML/CTF Rules 2025, which were remade in 2025 with new numbering, so an old rule reference no longer points at the provision it used to.
The CDD records are the identity information you collected, the verification evidence, and the method path: which method you used and the source references for the evidence. The customer due diligence page covers what counts as verified. Here the point is that the evidence and the method have to last the full seven years from the CDD record’s own anchor.
Reports are records too. An SMR is due within three business days of the suspicion forming (s41(2)(a)), five business days where some of the information may be privileged and the privilege belongs to someone other than the firm (s41(2)(aa)), and within 24 hours where the suspicion relates to terrorism financing. The report, the grounds behind it, and the assessment and reasoning all have to be retained. The suspicious matter reports page walks through the clock; here the point is that the file behind the report outlives the lodgement. A TTR is due within ten business days (s43(2)), and its records are the report and the transaction details it rests on, which s107 keeps for seven years from when they are made. Where privilege kept information out of a report, the documented assessment is the record, and it gets the same seven years and the same care with access.
Program records are the last group: your AML/CTF program, the risk assessment it sits on, and records of reviews and approvals. In practice these are what an independent evaluator asks for first.
The form requirement is about retrievability, not format. Records can be kept electronically; what matters is that you can retrieve and produce them for the full seven years. A scanned file in a shared drive satisfies that. A photo on a departing staff member’s phone does not. The test is simple: if the person who knows where a record is left tomorrow, can the firm still find it and produce it? If the answer is no, the record fails the obligation no matter how long it was kept.
What catches people out
The seven years runs from the record’s own anchor, not from the calendar year. If you archive by financial year, the destruction dates drift out of line with each record’s anchor. Some files are destroyed while their seven years still run, and a record destroyed early cannot be produced when a reviewer asks for it. The failure to retain is the breach; the later inability to produce is how it shows up.
The decision and its reasoning are records in their own right. Keep the identity documents and discard the notes, and the file shows what you collected but not what you decided. When a reviewer asks how you verified a customer, the note of what you checked and why you accepted the evidence answers more than the scan does. A file that holds only documents cannot demonstrate a decision at all, and that gap is what an examination will surface.
Records have to stay retrievable after the people who set them up leave. A shared drive whose folder permissions sit on one person’s account, a spreadsheet only a departing partner can open, a filing cabinet whose keys are in their desk: all of it stops working on the day that person walks out. The consequence is the same as never keeping the record, because producing it is the point of keeping it.
Access is a separate question for records connected to a report. The fewer people who can see an SMR file, the better. A file note visible to staff who deal with the customer can disclose the report’s existence, and a disclosure that would, or could reasonably be expected to, prejudice an investigation is the tipping-off offence under s123 of the Act. The maximum penalty is two years imprisonment, 120 penalty units, or both, and it does not matter whether an investigation has actually started.
What is still unsettled
The seven-year term is settled, the anchor for each group is settled, and so is the requirement to keep records in a retrievable form. What moves is the rule numbering underneath. The AML/CTF Rules 2025 were remade with new numbering, so a rule number from older guidance no longer points at the provision it used to. When you draft your own procedure, cite the 2025 instrument rather than a rule number lifted from material written before the remake.
Whether AUSTRAC will publish a dedicated record-keeping guidance note is also open. The form and retrievability requirements currently rest on general AUSTRAC guidance.
Where to start
If your firm has not worked through record-keeping yet, start here:
- Map the record types: list the groups in the table above against what your firm actually produces: transaction records, identity files, reports, program documents, and the decisions behind them. Assign each group an owner, usually your AML/CTF compliance officer (the AMLCO).
- Write the reasoning into the record: agree the capture format now: what was decided, on what evidence, by whom, and when. A template filled in at the time beats a note reconstructed from memory later.
- Test retrieval with a departure in mind: pick three records from last quarter and produce them the way a reviewer would, with the person who filed them out of the picture. Fix whatever fails.
How duely handles this
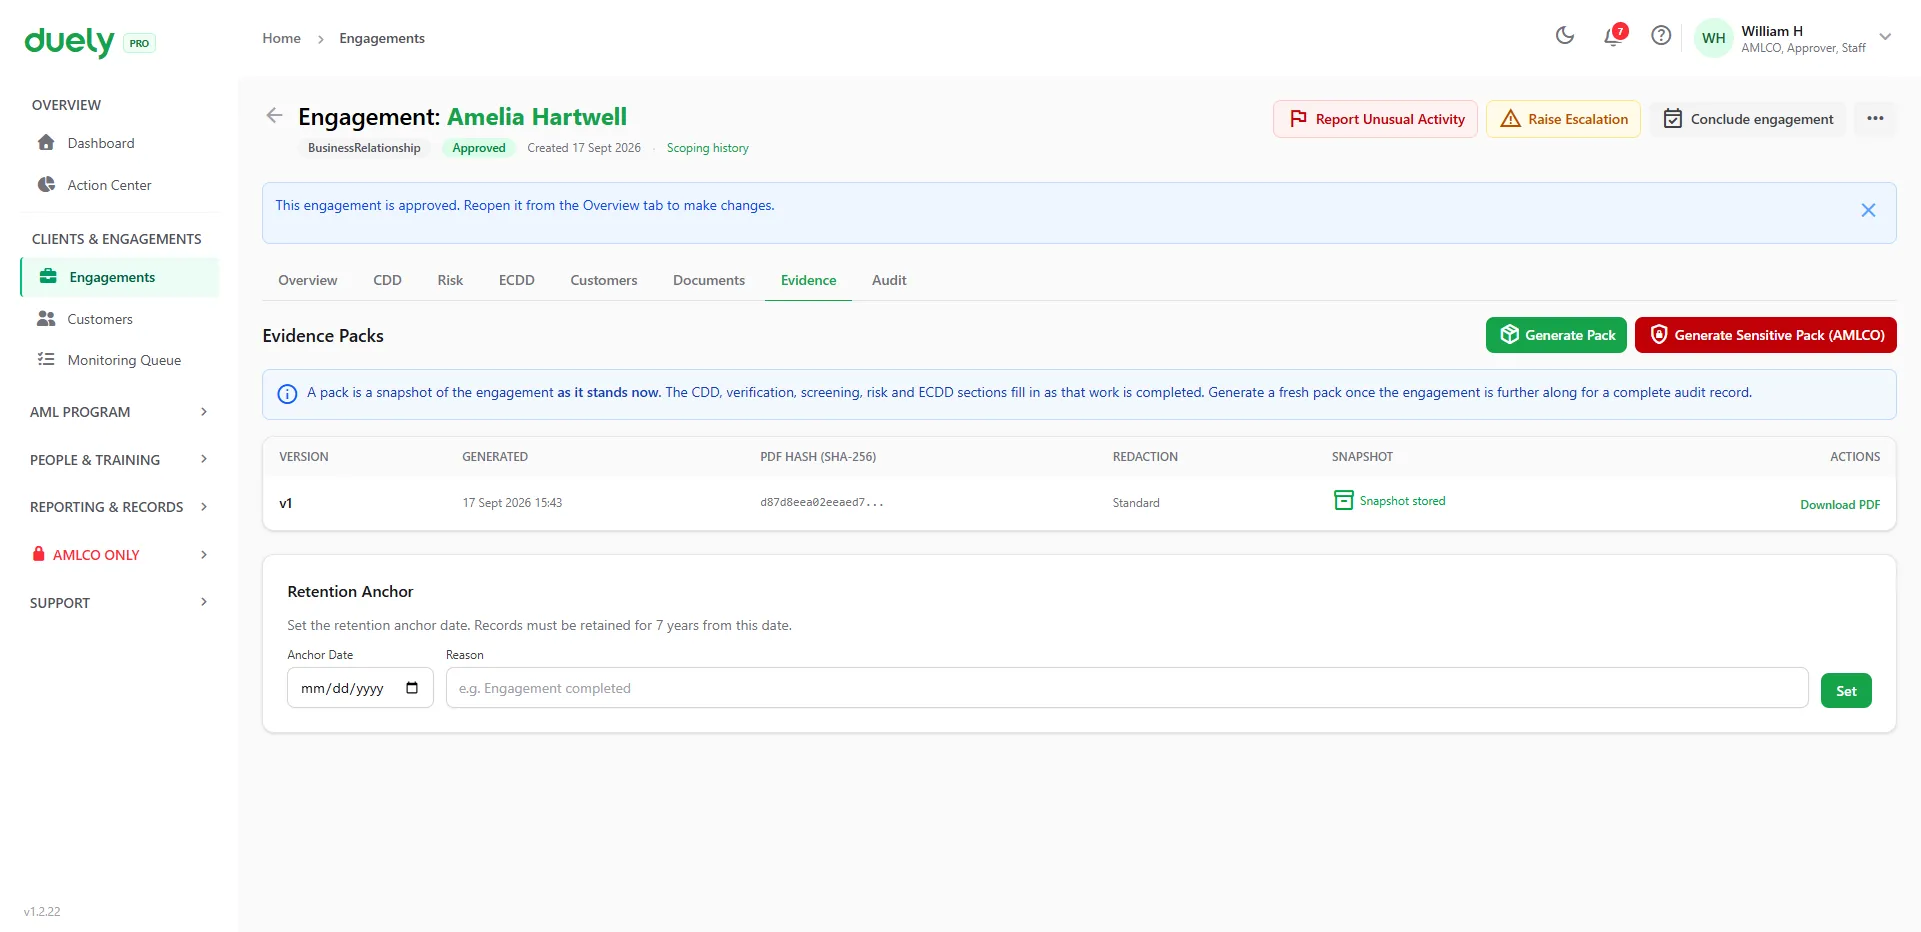
Concluding an engagement records a retention anchor (an end date and a reason), the date the seven years runs from, so the period is tied to the engagement rather than to a calendar year. The seven years is the legal requirement; duely records the anchor and does not calculate the period for you. The engagement end date is duely’s default anchor, not the statutory one: for CDD records the law runs the seven years from when the business relationship ends or the occasional transaction is completed (s 111), and program records have their own anchor (s 116). The audit log is held while your firm subscribes and stays read-only after the subscription ends, until the firm’s data is deleted (duely emails the administrator at least 30 days before that). It is append-only within the application: the application offers no way for any user, including the AMLCO, to edit or delete an entry. Evidence packs, generated on demand as a PDF, are versioned and hashed with SHA-256 when they are made, which is what makes it possible to show that a downloaded copy matches the hash recorded when the pack was made.